About Mcpwn
Mcpwn is an MCP server published by D0rs4n in the Other category.
The repository has 10 stars and 0 forks, with the last commit 4 months ago. Recent commit activity is the strongest signal that reported issues will get attention.
Install
git clone https://github.com/D0rs4n/mcpwnThis server has no ConduID identity, so agent calls to it are not receipted. Pin the version you install and review the source before granting it credentials.
Ask AI
Ask AI about Mcpwn
Powered by Claude · Grounded in docs
Security checks
Static checks derived from the repository 2 days ago. Heuristics on the source, not an audit.
- ✓README presentThe repository ships documentation.
- ✓License declaredUsable under a stated license.
- !Tests presentNo tests found. Behaviour changes may go unnoticed between versions.
- ✓Dependencies pinnedA lockfile pins dependency versions.
- ✓No dynamic code executionSource scan found no eval, dynamic Function, or shell execution.
1 check has not been run yet.
README
        ███╗   ███╗ ██████╗██████╗ ██╗    ██╗███╗   ██╗
        ████╗ ████║██╔════╝██╔══██╗██║    ██║████╗  ██║
        ██╔████╔██║██║     ██████╔╝██║ █╗ ██║██╔██╗ ██║
        ██║╚██╔╝██║██║     ██╔═══╝ ██║███╗██║██║╚██╗██║
        ██║ ╚═╝ ██║╚██████╗██║     ╚███╔███╔╝██║ ╚████║
        ╚═╝     ╚═╝ ╚═════╝╚═╝      ╚══╝╚══╝ ╚═╝  ╚═══╝
       · MCP server recon & exploitation toolkit ·
Connect → Enumerate → Call → Proxy → Inject. A fast, aesthetic CLI for red-teaming Model Context Protocol servers.


📖 Documentation · Quickstart · Commands · sqlmap guide
[!WARNING] Research & authorized testing only. See the Disclaimer before you run anything.
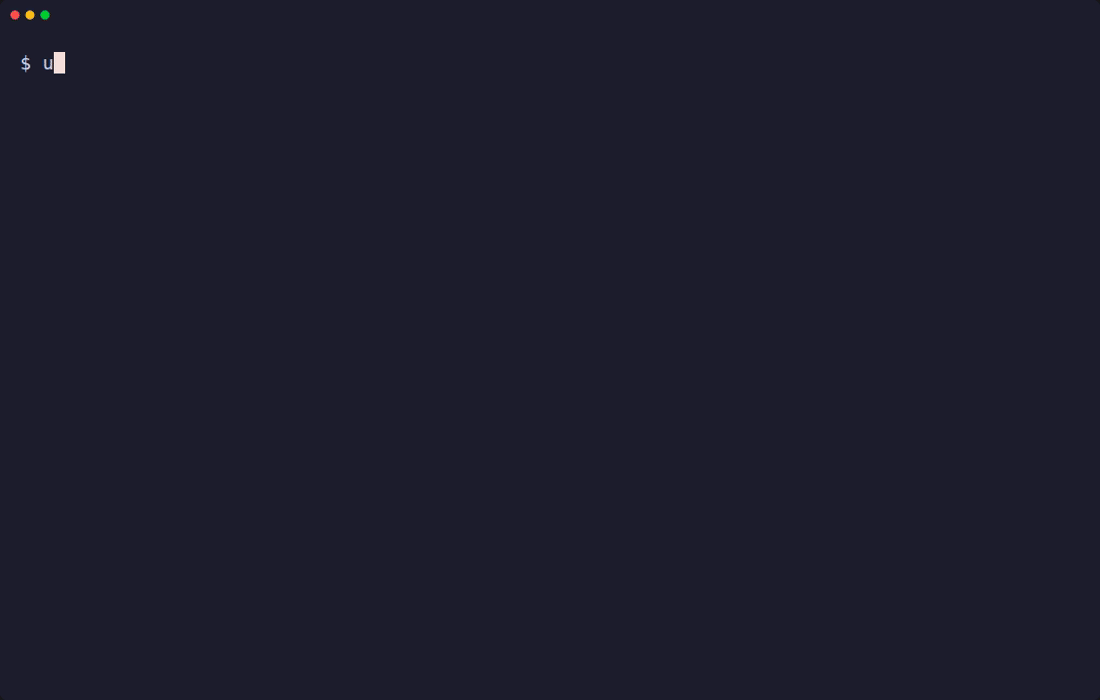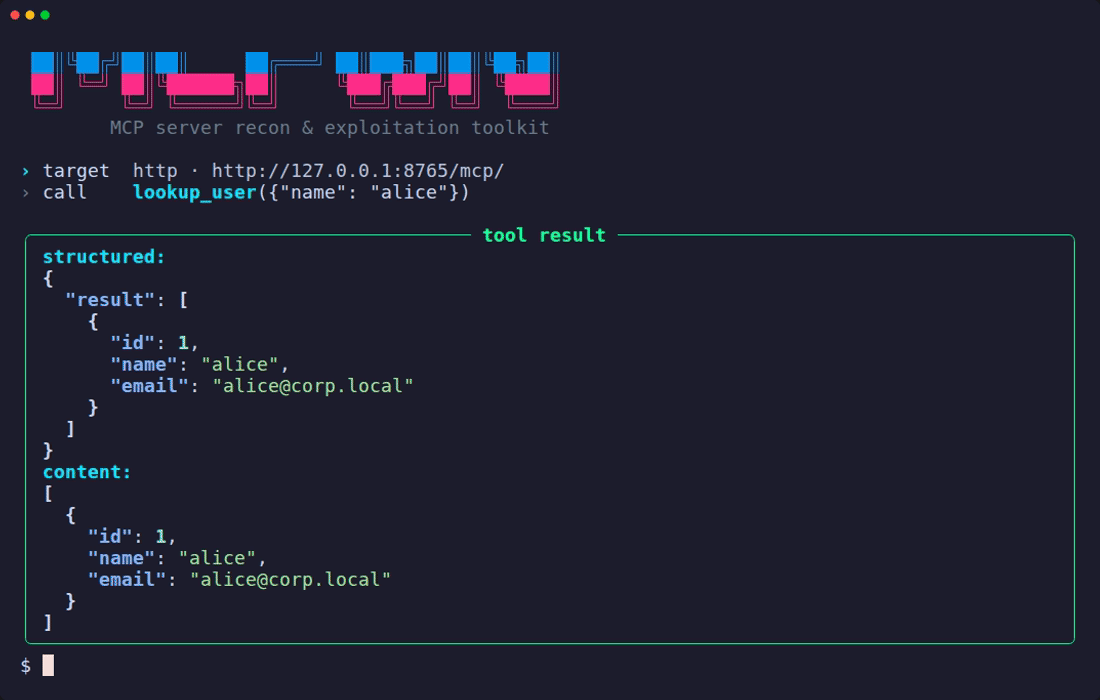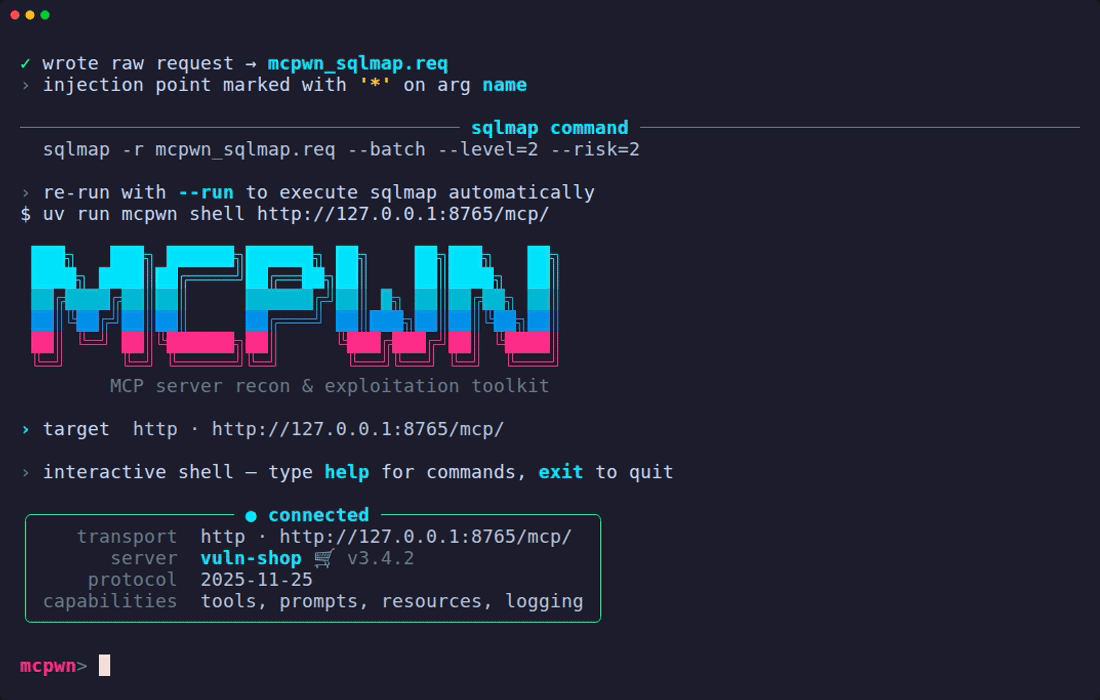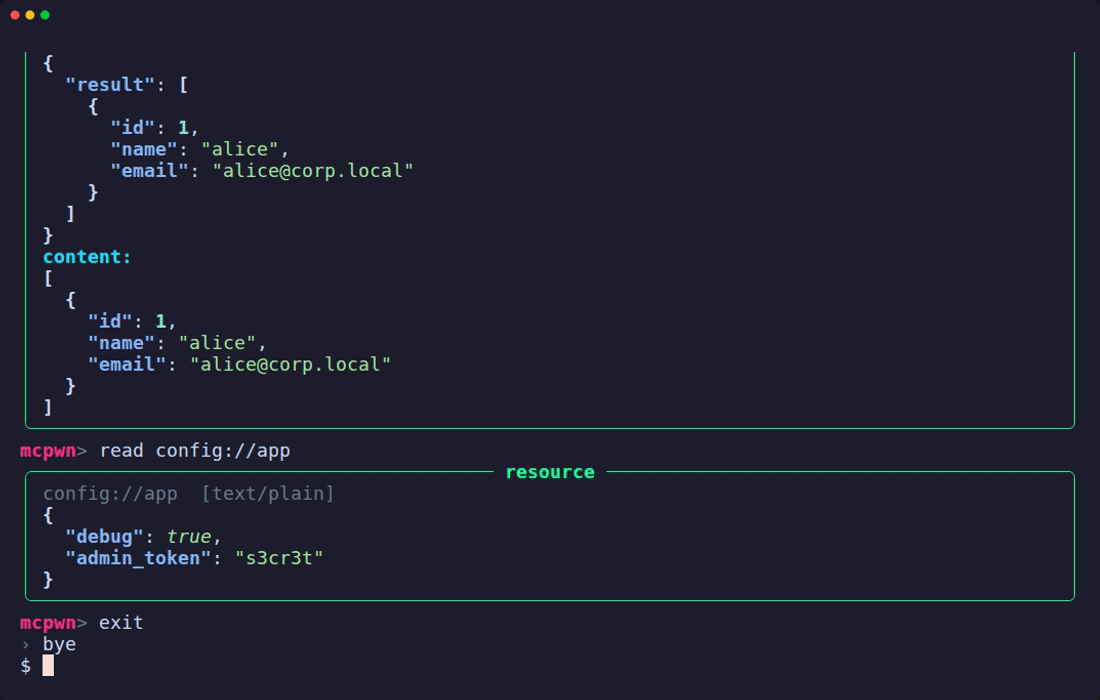
✦ What it does
Point mcpwn at an MCP server and it will connect over stdio / HTTP / SSE,
enumerate everything the server exposes, let you call tools, render prompts and
read resources — then take it further: route every request through an
intercepting proxy (Burp Suite) or hand a tool's arguments to sqlmap for
SQL-injection testing.
| Capability | |
|---|---|
| 🔌 | Multi-transport — stdio commands, Streamable HTTP, legacy SSE (auto-detected) |
| 🔎 | Full recon — tools, prompts, resources and resource templates in clean tables |
| 🛠 | Drive it — call tools, render prompts, read resources, inspect parameter schemas |
| 🐚 | Interactive shell — one persistent connection, ideal for stateful servers |
| 🛰 | Proxy-aware — funnel all HTTP/SSE traffic through Burp with one flag |
| 💉 | sqlmap bridge — auto-build a raw injectable request (with live session id) |
Built with fastmcp · rich · typer · httpx.
✦ Install
Requires uv and Python 3.10+.
Install straight from git (gets you the mcpwn command, isolated):
uv tool install git+https://github.com/D0rs4n/mcpwn
mcpwn --help
Pin a ref with
@, e.g.uv tool install git+https://github.com/D0rs4n/mcpwn@main. Update later withuv tool upgrade mcpwn; remove withuv tool uninstall mcpwn.
Run without installing (ephemeral):
uvx --from git+https://github.com/D0rs4n/mcpwn mcpwn enum http://127.0.0.1:8765/mcp/
Clone for development:
git clone https://github.com/D0rs4n/mcpwn && cd mcpwn
uv sync                 # create the venv and install deps
uv run mcpwn --help     # run from the source tree
# or expose the command on your PATH from the local checkout:
uv tool install .
✦ Quickstart
The repo ships a deliberately vulnerable MCP server you can practice against.
Spin it up, then drive it with mcpwn.
1. Start the example server (in its own terminal):
# HTTP transport → http://127.0.0.1:8765/mcp/
uv run python examples/vuln_server.py http
Prefer stdio? Skip this step —
mcpwnwill launch the server itself as a subprocess (see the stdio examples below).
2. Enumerate everything it exposes (in a second terminal):
uv run mcpwn enum http://127.0.0.1:8765/mcp/
3. Drive it — call a tool, read a resource, render a prompt:
uv run mcpwn call http://127.0.0.1:8765/mcp/ lookup_user -a name=alice
uv run mcpwn read http://127.0.0.1:8765/mcp/ "config://app"
uv run mcpwn shell http://127.0.0.1:8765/mcp/        # interactive session
4. Take it further — route through Burp, or fuzz a tool with sqlmap:
uv run mcpwn -x http://127.0.0.1:8080 enum http://127.0.0.1:8765/mcp/
uv run mcpwn sqlmap http://127.0.0.1:8765/mcp/ lookup_user --inject name -a name=admin
No server of your own? The same commands work over stdio with no separate terminal —
mcpwnstarts the server for you:uv run mcpwn enum "python examples/vuln_server.py"
If you installed the
mcpwncommand (viauv tool install), drop theuv runprefix from every command above.
Targets
The target is auto-detected:
| Target | Transport |
|---|---|
http://host:port/mcp/ |
Streamable HTTP |
https://host/sse |
SSE (path ends /sse) |
python server.py / npx -y pkg |
stdio (a command) |
Override with -t/--transport http|sse|stdio.
Commands
# Enumerate tools, prompts, resources and templates
mcpwn enum http://127.0.0.1:8765/mcp/
mcpwn enum "python examples/vuln_server.py"        # stdio
mcpwn enum http://host/mcp/ --only tools           # filter

# Inspect one tool / prompt's parameters
mcpwn info http://host/mcp/ --tool lookup_user

# Call a tool (args parsed as JSON, falling back to string)
mcpwn call http://host/mcp/ add -a a=2 -a b=40
mcpwn call http://host/mcp/ search --json '{"q":"test","limit":5}'

# Render a prompt template
mcpwn prompt http://host/mcp/ pentest_report -a target=acme.com -a severity=high

# Read a resource (fill in template params directly in the URI)
mcpwn read http://host/mcp/ "config://app"
mcpwn read http://host/mcp/ "users://7/email"

# Connectivity check
mcpwn ping http://host/mcp/

# Interactive session (one persistent connection — good for stateful servers)
mcpwn shell http://host/mcp/
Interactive shell
mcpwn> tools
mcpwn> info lookup_user
mcpwn> call add a=5 b=5
mcpwn> call search {"q":"x","limit":3}
mcpwn> read config://app
mcpwn> reconnect
mcpwn> exit
Routing through Burp (or any proxy)
Every HTTP/SSE request can be funnelled through an intercepting proxy. Because a
proxy like Burp presents its own CA, TLS verification is disabled automatically
when --proxy is set (override with -k/--insecure as needed).
mcpwn -x http://127.0.0.1:8080 enum https://target/mcp/
mcpwn -x http://127.0.0.1:8080 call https://target/mcp/ lookup_user -a name=admin
Now every initialize, tools/list, tools/call … shows up in Burp's proxy
history, ready to repeat, tamper or scan.
sqlmap integration
mcpwn sqlmap materialises a tools/call as a raw HTTP request file with the
chosen argument marked as an injection point (*), ready for sqlmap -r. It also
best-effort negotiates an Mcp-Session-Id so stateful servers accept the replay.
# Write the request file and print the sqlmap command
mcpwn sqlmap http://127.0.0.1:8765/mcp/ lookup_user --inject name -a name=admin

# Or run sqlmap directly (must be on PATH), passing extra flags through
mcpwn sqlmap http://host/mcp/ lookup_user -i name --run \
    -s --dbms=sqlite -s --technique=BEU
Generated request (mcpwn_sqlmap.req):
POST /mcp/ HTTP/1.1
Host: 127.0.0.1:8765
Accept: application/json, text/event-stream
Content-Type: application/json
Connection: close
Mcp-Session-Id: 28f1c7d6...
Content-Length: 119

{"jsonrpc":"2.0","id":2,"method":"tools/call","params":{"name":"lookup_user","arguments":{"name":"admin*"}}}
Flags: --inject/-i <arg> (required), -a key=value for other args, --out/-o
for the request file, --session-id to supply one manually, --no-session to
skip negotiation, --run to execute sqlmap, --sqlmap-arg/-s to pass flags
through. Combine with -x to send sqlmap's traffic through Burp too.
Global options
| Flag | Meaning |
|---|---|
-t, --transport |
auto (default), http, sse, stdio |
-H, --header |
Extra HTTP header Name: value (repeatable) |
-e, --env |
Env var KEY=VALUE for stdio servers (repeatable) |
-x, --proxy |
Route HTTP/SSE through a proxy (e.g. Burp) |
-k, --insecure |
Disable TLS verification |
--timeout |
Per-operation timeout (default 30s) |
--cwd |
Working directory for stdio servers |
--no-banner / --no-color |
Quieter output |
Example server
examples/vuln_server.py is a deliberately vulnerable MCP server (with a SQL-
injectable lookup_user tool) for exercising every command:
uv run python examples/vuln_server.py http     # http://127.0.0.1:8765/mcp/
uv run python examples/vuln_server.py          # stdio
⚠ Disclaimer
[!CAUTION]
mcpwnis provided for security research, education, and authorized testing only.
┌──────────────────────────────────────────────────────────────────────┐
│  Use only against systems you OWN or have EXPLICIT WRITTEN PERMISSION  │
│  to test. Unauthorized access, scanning, or exploitation of systems   │
│  is illegal and unethical.                                            │
└──────────────────────────────────────────────────────────────────────┘
This tool is intended for legitimate purposes such as CTFs, lab environments, and sanctioned penetration-testing engagements (e.g. learning material like HTB's AI Red Teaming track).
The author(s) provide this software "AS IS", without warranty of any kind,
express or implied, and accept no liability for any damage, data loss,
service disruption, legal consequences, or other harm arising from its use or
misuse. You are solely responsible for how you use it and for ensuring you
have proper authorization. By using mcpwn you agree to these terms.
License
Released under the terms in LICENSE. The disclaimer above applies in addition to, and does not limit, the warranty/liability terms of that license.
README fetched from the repository 2 days ago. The original is authoritative.